Cybersecurity consulting · Map. Test. Defend.
Map what matters. Test what you trust. Defend what you’ve built.
Software changes bring new security risks. AI adds its own, including prompt injection and exposure of sensitive information.
We help you find and fix security weaknesses in your software, infrastructure, and AI systems.
We call this Map, Test, and Defend. First, we understand how your systems work and what needs protecting. Then we test for weaknesses, question assumptions, and identify risks. Finally, we help address vulnerabilities and strengthen your defenses.
Security is an ongoing process. As systems and threats change, we return to it.
How we work
| Step | Stage | What happens |
|---|---|---|
| 01 | Map | Understand your software, infrastructure, and AI systems. Identify important assets, how information flows, who has access, and where security risks might exist. |
| 02 | Test | Examine code, configurations, and security controls. Test for vulnerabilities, including traditional software weaknesses and AI-specific risks such as prompt injection, data exposure, and unsafe integrations. |
| 03 | Defend | Prioritize findings, fix vulnerabilities, and strengthen protections. Verify that improvements work and establish practices to keep systems secure as they change. |
Application security reviews
A review tests how your application protects customer data. Depending on the scope, that includes API permissions, session handling, source code, and deployment settings, using OWASP requirements to guide the checks.
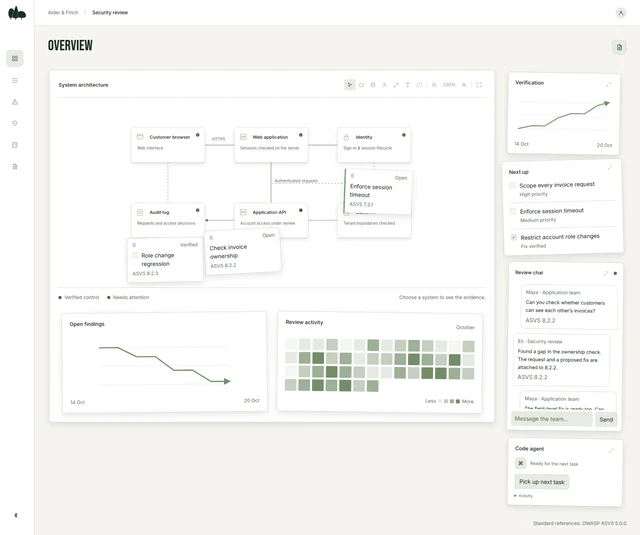
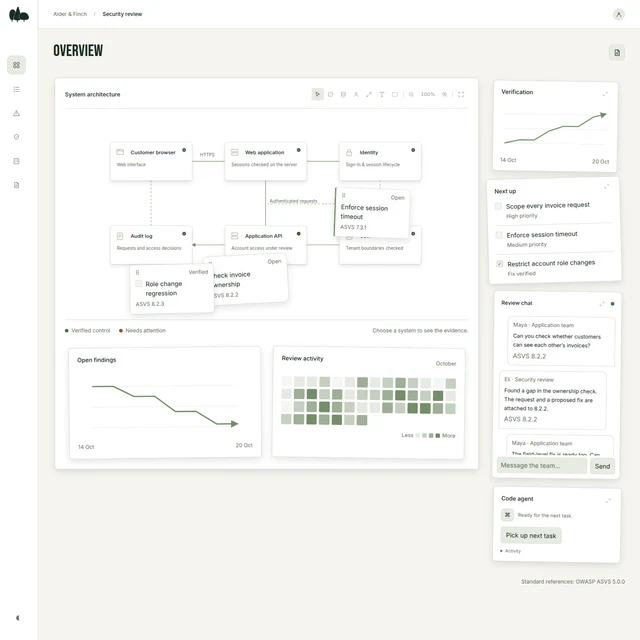
You get access to a custom app to follow the findings as the review develops and discuss fixes with your team. The final PDF report records the results and any issues that still need work.
Security projects
Know what you’re protecting
You can’t secure what you don’t understand. We examine how systems fit together, where information goes, and what matters most to your business.
Test, don’t assume
Security tools and policies don’t guarantee protection. We test systems and verify that safeguards work rather than assuming they’re effective.
Understand new threats
AI introduces new vulnerabilities alongside traditional software risks. We keep up with emerging threats and testing techniques as technology evolves.
Fix what matters
Some vulnerabilities pose more risk than others. We help you decide what to fix first based on how your systems are used and what could be exposed.
Build security into software
We help your team include security checks in development and maintenance, so you can catch problems before they reach production.
Keep improving
Your systems need checking as software changes and new vulnerabilities emerge. We help you reassess risks and update protections over time.
Pricing
| Arrangement | How it works |
|---|---|
| Security assessments and consulting | We work on a per-project basis. Each engagement begins with an agreed scope, whether that’s an application security review, AI security assessment, infrastructure review, or help addressing identified vulnerabilities. We agree on the work and price before starting. |
Let’s make it secure.
Building something new, introducing AI, or concerned about the security of an existing system? Tell us a little about what you’d like to protect.